Tuesday, December 5, 2017

How To Become A Millionaire With Bitcoin


Becoming a millionaire will be a dream for many of the people. Everyone wants to be rich but one cannot simply become millionaire without working smart and hard. If are capable of working smart and hard then you have a plenty of chances in the world to become rich. Let me come into the main topic of becoming a millionaire with bitcoin.
Bitcoin is the world’s best and highest market valued decentralized block chain network. There are plenty of ways to earn bitcoin. In this topic we are going to discuss the ways to earn bitcoins. Let’s go.
First things first, there are plenty of sites which pays you bitcoin for free if you work for them. Well, they don’t pay you much and its not easy to become a millionaire with this sites. Read the complete article to choose the right option of making bitcoin.
The second option is through investment and trading. Trading is one of the toughest job in the world. If you trade without a proper knowledge and experience, then you may loose up all the money.
Let’s get on to the real and best ways of making bitcoin. Let me clear you one thing. If you are scared of doing this or if you are scared of little investments then that’s the biggest mistake you are doing in life. Make a proper research and have a good faith in what you are doing. I am mentioning it again ‘don’t be scared to do the things’.
Network marketing is the greatest key for plenty of millionaires in the world. A billionaire once said (I explained my plan to 1200 people, 900 of them rejected, 300 of them listened, 60 of them joined, 10 people believed me and made me billionaire). What all you require in this business is patience and a very little investment.
The most important thing is to choose the right network to start your network marketing. As we are talking about bitcoin here so we need to choose a good platform related to bitcoin. I am mentioned a link to signup for the network marketing. You can signup for free then you will get a call from the team and they will explain you about the details of problem.

This is the link to route of success. This network chain made plenty of millionaires in India. So you might be getting a doubt, Why should I trust this network? We do have the answer for this. We have invested in website and continued the chain for a decent period.This network had paid 30 lakhs for my investors. There are people who got the amount in crores. When you Signup for this network you can the plans. There are presentations which will clarity all you doubts. The company is legally registered in UK and USA. If you would like to know more about the company you can visit our further links. We have provided a clear payment proof and review of the company

Monday, December 4, 2017

How to Magento 2.1.3 run on PHP 7.1.0

Here is how to install and run the latest Magento 2.1.3 on the latest PHP 7.1.0.
Disclaimer: although this hack is tested on the default Magento 2.1.3 sample data installation use this with caution for production sites. always test test test!

1. Patch installation files


Magento 2.1.3 checks php version and refuses to install with php 7.1.0. Let's bypass it.
Open up setup/src/Magento/Setup/Model/PhpRedinessCheck.php and change line 79

from:
$normalizedPhpVersion = $this->getNormalizedCurrentPhpVersion(PHP_VERSION);
to:
$normalizedPhpVersion = $this->getNormalizedCurrentPhpVersion('7.0.2');


2. Suppress mcrypt warnings

Edit vendor/magento/framework/Encryption/Crypt.php and prefix all mcrypt/mdecrypt functions with @ :
@mdecrypt_generic
here is a diff file:


54c54
<         $this->_handle = @mcrypt_module_open($cipher, '', $mode, '');
---
>         $this->_handle = mcrypt_module_open($cipher, '', $mode, '');
56c56
<             $maxKeySize = @mcrypt_enc_get_key_size($this->_handle);
---
>             $maxKeySize = mcrypt_enc_get_key_size($this->_handle);
62c62
<             $initVectorSize = @mcrypt_enc_get_iv_size($this->_handle);
---
>             $initVectorSize = mcrypt_enc_get_iv_size($this->_handle);
80c80
<             @mcrypt_module_close($this->_handle);
---
>             mcrypt_module_close($this->_handle);
83c83
<         @mcrypt_generic_init($this->_handle, $key, $initVector);
---
>         mcrypt_generic_init($this->_handle, $key, $initVector);
93,94c93,94
<         @mcrypt_generic_deinit($this->_handle);
<         @mcrypt_module_close($this->_handle);
---
>         mcrypt_generic_deinit($this->_handle);
>         mcrypt_module_close($this->_handle);
138c138
<         return @mcrypt_generic($this->_handle, $data);
---
>         return mcrypt_generic($this->_handle, $data);
152c152
<         $data = @mdecrypt_generic($this->_handle, $data);
---
>         $data = mdecrypt_generic($this->_handle, $data);


clear cache:
rm -rf var/cache/*
rm -rf var/generation/*
and enjoy!

Tuesday, November 21, 2017

Working with Hive and HDFS

Hello Guys,

Today we are learning how to deal with hive and HDFS in hadoop system.

First start hive server 2 and metadata for working with Hive. after starting hive client follow below commands:

Create table in Hive


CREATE TABLE NEWTERRITORIES (CID string,FAMILY_NAME string,FULLNAME string,ADDRESS string,DISTRICT string,REGION string,PHONE_NUMBER string,MOBILE_NUMBER string) row format delimited fields terminated by '\t' stored as textfile;


Using HDFS command:
Make directory on HDFS

hdfs dfs -mkdir /user/hadoop/hongkong/NEWTERRITORIES/


Upload file from local to HDFS system

hdfs dfs -copyFromLocal /mnt/data/hongkong/NEWTERRITORIES.tsv /user/hadoop/hongkong/NEWTERRITORIES/

Hive commnad:
Load data from HDFS to hive table

LOAD DATA INPATH '/user/hadoop/hongkong/NEWTERRITORIES/NEWTERRITORIES.tsv' INTO TABLE NEWTERRITORIES;


Create index in Hive data

CREATE INDEX NEWTERRITORIES_index ON TABLE NEWTERRITORIES (CID,FAMILY_NAME,FULLNAME,ADDRESS,DISTRICT,REGION,PHONE_NUMBER,MOBILE_NUMBER) AS 'org.apache.hadoop.hive.ql.index.compact.CompactIndexHandler' WITH DEFERRED REBUILD;

Get records from table:

select * from NEWTERRITORIES;


Hive evidence can be identified through HiveQL commands. The following commands can be used to get a full listing of all databases and tables as well as the table's formats:


Description
SHOW DATABASES;
This lists all available databases
SHOW TABLES;
This lists all tables in current database
USE databaseName
This makes databaseName the current database
DESCRIBE (FORMATTED|EXTENDED) table
This lists the formatting details about


For more information like connect hive with Programming language (PHP, Java) we will learn in next tutorial. 

Wednesday, April 5, 2017

Setup Laravel Login Authentication In Simple And Easy Steps


Step 1: Setup the Database

  • Click on Launch Database.
  • Click on Create Table. Name the new table users and select innoDB andascii_general
  • Add the following columns in the table:
    • id (int)   (Check AutoIncrement A.I.)
    • name (text)
    • username (text)
    • email (text)
    • password (text)
    • remember_token (text)
    • timestamp (time)
  • Click Save
  • Now Click New Item and then add the following user:
    • Name: Jaymin
    • Username: jayminlimbachiya
    • Email: jay.120421@gmail.com
    • Password: password
  • Click Save

Step 2: Setup the Routes

Edit below file

routes.php
<?php
/*
| Application Routes
*/
// route to show the login form
Route::get('login', array(
'uses' => 'MainController@showLogin'
));
// route to process the form
Route::post('login', array(
'uses' => 'MainController@doLogin'
));
Route::get('logout', array(
'uses' => 'MainController@doLogout'
));
Route::get('/',
function ()
{
return view('welcome');
});

Step 3: Make the Controllers

Create:
app/Http/Controllers/MainController.php


I will extend MainController from the Base Controller and make three functions to show login, check the login and for logging out.

Following is the code for MainController:

<?php
namespace AppHttpControllers;

use Redirect;
use Auth;
use Input;
use IlluminateSupportFacadesValidator;
use IlluminateFoundationBusDispatchesJobs;
use IlluminateRoutingController as BaseController;
use IlluminateFoundationValidationValidatesRequests;
use IlluminateFoundationAuthAccessAuthorizesRequests;
use IlluminateFoundationAuthAccessAuthorizesResources;
use IlluminateHtmlHtmlServiceProvider;

class MainController extends BaseController
{

public


function showLogin()
{

// Form View

return view('login');
}

public

function doLogout()
{

Auth::logout(); // logging out user
return Redirect::to('login'); // redirection to login screen

}

public function doLogin()
{

// Creating Rules for Email and Password

$rules = array(
'email' => 'required|email', // make sure the email is an actual email
'password' => 'required|alphaNum|min:8'


// password has to be greater than 3 characters and can only be alphanumeric and);
// checking all field

$validator = Validator::make(Input::all() , $rules);

// if the validator fails, redirect back to the form

if ($validator->fails())
{

return Redirect::to('login')->withErrors($validator) // send back all errors to the login form
->withInput(Input::except('password')); // send back the input (not the password) so that we can repopulate the form

}
else
{
// create our user data for the authentication
$userdata = array(
'email' => Input::get('email') ,
'password' => Input::get('password')
);

// attempt to do the login
if (Auth::attempt($userdata))
{

// validation successful
// do whatever you want on success
}
else
{

// validation not successful, send back to form
return Redirect::to('checklogin');
}
}
}

  }


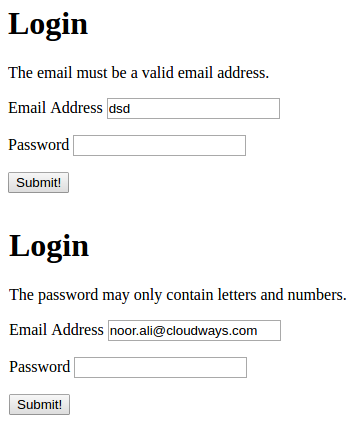
Step 4: Setup the View

$ resources/views/checklogin.blade.php


Here is the HTML code for this file.

<!doctype html>
<html>
<head>
<title>My Login Page</title>
</head>
<body>
<
{{ Form::open(array('url' => 'login')) }}
<h1>Login</h1>
<!-- if there are login errors, show them here -->
<p>
{{ $errors->first('email') }}
{{ $errors->first('password') }}
</p>
<p>
{{ Form::label('email', 'Email Address') }}
{{ Form::text('email', Input::old('email'), array('placeholder' => 'check@jaym.in')) }}
</p>
<p>
{{ Form::label('password', 'Password') }}
{{ Form::password('password') }}
</p>
<p>{{ Form::submit('Submit!') }}</p>

{{ Form::close() }}


This is simple example of laravel login authentication. if you have any query or suggestion please comment below or email me: jay.120421@gmail.com

Monday, August 8, 2016

PDF parsing using pdfparser

PdfParser, a standalone PHP library, provides various tools to extract data from a PDF file.
Currently, secured documents are not supported.
This Library is still under active development. As a result, users must expect BC breaks when using the master version.

Prerequisites

This library requires PHP 5.3.
PDFParser is built on top of TCPDF parser.
This library will be automatically downloaded through Composer command line.

Installation

Using Composer

Add PDFParser to your composer.json file :
{
    "require": {
        "smalot/pdfparser": "*"
    }
}
Now ask for composer to download the bundle by running the command:
$ composer update smalot/pdfparser

As standalone library

First of all, download the library from Github by choosing a specific release or directly the master.
Once done, unzip it and run the following command line using composer.
composer update
This command will download any dependencies (Atoum library) and create the 'autoload.php' file.
Now create a new file with this content, in the same folder :
<?php

// Include 'Composer' autoloader.
include 'vendor/autoload.php';

// Your code
// ...

?>

Unit tests with Atoum

Run Atoum unit tests (with code coverage - if xdebug installed) :
$ vendor/bin/atoum -d vendor/smalot/pdfparser/src/Smalot/PdfParser/Tests/
Once this command is ended, the folder "coverage/" will contain html pages with a code coverage summary.

Use

This sample will parse all the pdf file and extract text from each page.
<?php

// Include Composer autoloader if not already done.
include 'vendor/autoload.php';

// Parse pdf file and build necessary objects.
$parser = new \Smalot\PdfParser\Parser();
$pdf    = $parser->parseFile('document.pdf');

$text = $pdf->getText();
echo $text;

?>
You can too extract text from each page handly or for a specific page.

Download demo here

Monday, August 1, 2016

How do I enable functions, procedures, and triggers for my Amazon RDS MySQL instance?

I need to enable functions, procedures, and triggers for an instance of MySQL on Amazon RDS. How can I do this?
To use functions, procedures, or triggers when binary logging is enabled requires the MySQL SUPER privilege, which is restricted for RDS MySQL DB instances.
You can can enable functions, procedures, and triggers when binary logging is enabled without the SUPER privilege by setting thelog_bin_trust_function_creators parameter to true for the DB parameter group that you create for your MySQL instance(s).
Note
A default DB parameter group is created if you create a DB instance without specifying a DB parameter group that you create. This group contains database engine defaults and Amazon RDS system defaults based on the engine, compute class, and allocated storage of the instance. You cannot modify the parameter settings of a default DB parameter group; you must create your own DB parameter group to change parameter settings from their default value. Note that not all DB engine parameters can be changed in a DB parameter group that you create.
  1. Sign in to the AWS Management Console and open the Amazon RDS console at https://console.aws.amazon.com/rds/
  2. In the navigation pane, choose Parameter Groups.
  3. Choose Create Parameter Group. The Create Parameter Group window appears.
  4. For Parameter Group Family, choose the parameter group family.
  5. For Group Name, type the name of the new DB parameter group.
  6. For Description, type a description for the new DB parameter group.
  7. Choose Create.
Important
After you create a DB parameter group, you should wait at least 5 minutes before creating your first DB instance that uses that DB parameter group.
For more information about creating a DB parameter group, see Working with DB Parameter Groups - Creating a DB Parameter Group.
  1. In the navigation pane, choose Parameter Groups. The available DB parameter groups appear in a list.
  2. In the list, select the parameter group you want to modify.
  3. Choose Edit Parameters and set the following parameter to the specified value:
        log_bin_trust_function_creators = 1
  4. Choose Save Changes.
Important
After you modify a DB parameter group, you should wait at least 5 minutes before creating your first DB instance that uses that DB parameter group.
For information about modifiying a DB parameter group, see Working with DB Parameter Groups - Modifying Parameters in a DB Parameter Group.
  1. In the navigation pane, choose Instances.
  2. Select the DB instance you want to associate with a DB parameter group.
  3. On the Instance Actions menu, choose Modify.
  4. In the Modify DB Instance dialog box, under Database Options, choose the parameter group you want to associate with the DB instance. Changing this setting does not result in an outage. The parameter group name changes immediately, but the actual parameter changes are not applied until you reboot the instance without failover.
  5. Apply changes by rebooting the instance.
Amazon RDS, MySQL, error 1419, create functions, super privilege, CURRENT_USER, stored procedure, DB parameter group, triggers, binary logging